
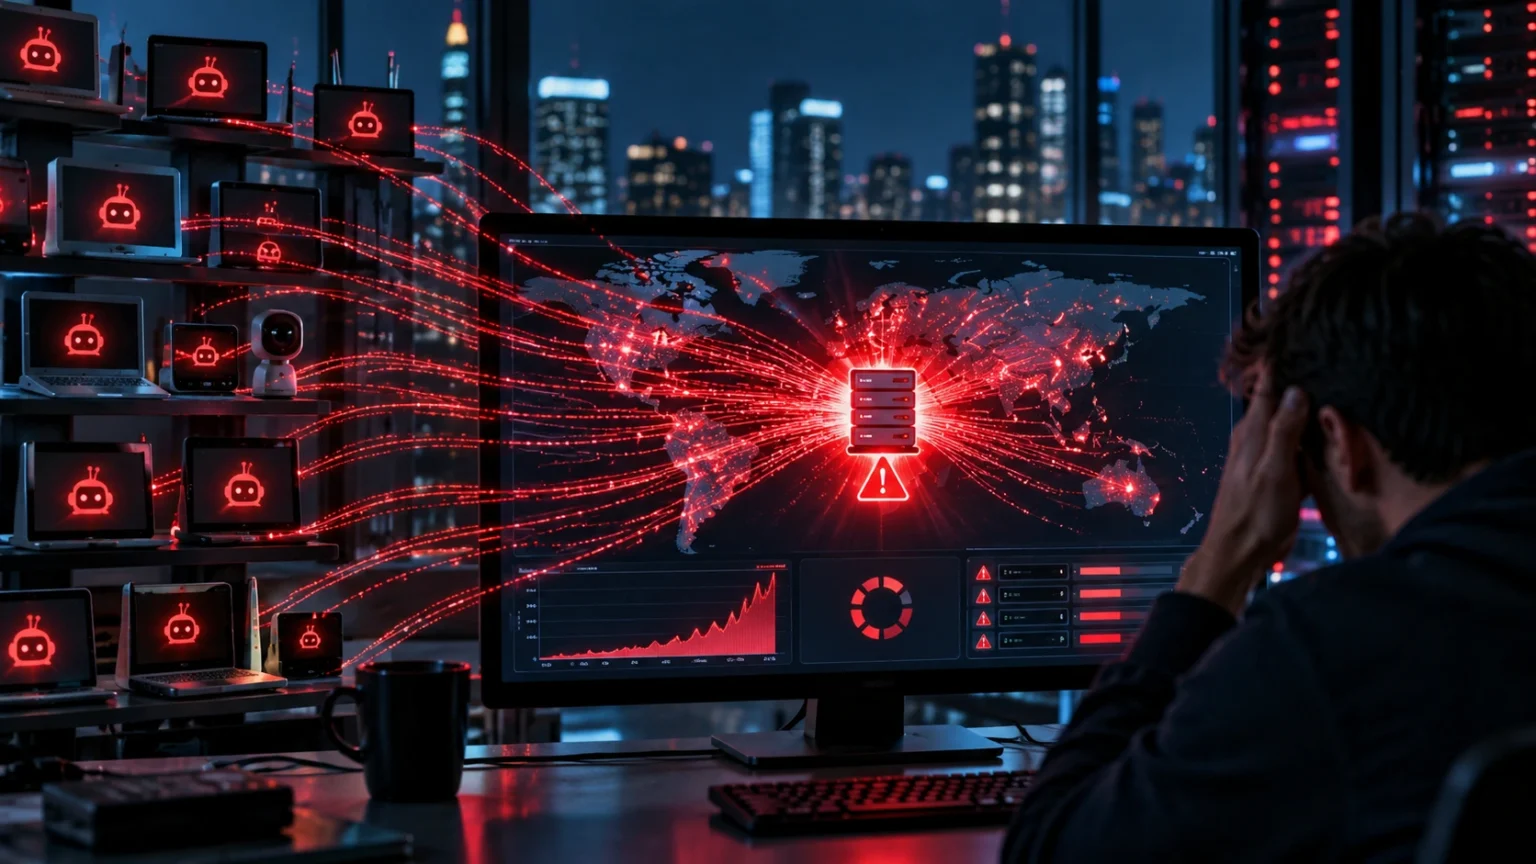
A Distributed Denial-of-Service attack, commonly called a DDoS attack, is a cybersecurity threat designed to make a website, application, or online service unavailable to legitimate users. Instead of stealing information directly, the attacker overwhelms the target with more traffic or requests than it can handle. The result may be severe slowdowns, connection failures, or complete service disruption.
DDoS attacks can affect businesses of every size, from small ecommerce websites to large online platforms and infrastructure providers. Understanding how these attacks work helps organizations recognize warning signs and prepare suitable defenses. While the technical methods vary, the basic goal remains the same: exhaust available resources so genuine users struggle or fail to access the service.
What Is a DDoS Attack?
A DDoS attack happens when traffic from many different devices is directed toward one target at the same time. The target may be a website, web server, application, network, or another internet-facing service. When the incoming traffic exceeds available capacity, legitimate requests may experience delays, errors, or complete failure.
The word “distributed” is important because the unwanted traffic comes from multiple sources rather than one computer. These sources may include compromised computers, smartphones, servers, routers, or other internet-connected devices. Using many systems makes the attack harder to block because malicious requests do not necessarily originate from one easily identifiable address.
Unlike a traditional hacking attempt, a DDoS attack does not always require the attacker to gain direct access to the target’s data or administrative systems. The primary objective is availability disruption. However, DDoS activity can still create serious financial and operational consequences when customers, employees, or partners cannot reach important online services.
How Does a DDoS Attack Work?
Every online service has practical limits on how much traffic, processing, memory, and network bandwidth it can handle at once. Normal traffic stays within those limits most of the time. A DDoS attack attempts to push activity beyond those limits by creating unusually large volumes of unwanted requests or network traffic.
As resources become consumed, the server or network may struggle to respond to legitimate visitors. Pages might load slowly, applications may time out, and users can start seeing connection errors. In severe cases, infrastructure can become completely unavailable until attack traffic decreases or defensive systems successfully filter and absorb it.
The situation is similar to overwhelming a customer service center with an enormous number of meaningless calls. Real customers can no longer reach available agents even though the service itself has not been destroyed. DDoS attacks use this same principle digitally by consuming the capacity required to serve legitimate internet users.
What Is a Botnet in a DDoS Attack?
Many DDoS attacks involve a botnet, which is a collection of compromised internet-connected devices controlled remotely. Individual device owners may not even realize their systems have become part of a malicious network. Computers, servers, routers, cameras, and poorly secured Internet of Things devices can potentially be abused after compromise.
The attacker can instruct large numbers of infected devices to communicate with the same target around the same time. Because the requests originate from many different systems and locations, distinguishing malicious traffic from real visitors becomes more complicated. The combined traffic may be far greater than any single attacking computer could generate alone.
Strong device security helps reduce the pool of systems criminals can potentially misuse. Changing default passwords, applying software updates, restricting unnecessary internet exposure, and removing unsupported devices can all improve protection. Botnet prevention matters beyond protecting one device because compromised equipment can potentially be used to harm unrelated services elsewhere on the internet.
Main Types of DDoS Attacks
DDoS attacks are commonly grouped into categories based on which resource they attempt to overwhelm. Volumetric attacks focus on consuming large amounts of network bandwidth. When incoming traffic fills available capacity, legitimate communications may struggle to reach the targeted service even if its application servers are otherwise functioning normally.
Protocol-focused attacks attempt to exhaust network or infrastructure resources involved in processing connections. Rather than simply sending as much raw traffic as possible, these attacks create conditions that place pressure on systems responsible for handling communication. Defensive infrastructure may become overloaded while trying to manage large numbers of abnormal or incomplete requests.
Application-layer attacks focus on specific online services, such as websites or APIs. They may resemble ordinary user requests but arrive in volumes designed to consume application resources. These attacks can sometimes be difficult to recognize because the traffic may look more realistic than obviously abnormal network floods.
Common Signs of a DDoS Attack
One common warning sign is a sudden and unexplained increase in traffic. A legitimate marketing campaign or viral post can also create traffic spikes, so increased visits alone do not prove an attack. Security teams need to examine where traffic is coming from, what it is requesting, and whether its behavior matches normal users.
Repeated connection failures, unusually slow pages, application timeouts, or unavailable services can also indicate resource exhaustion. Monitoring tools may show extremely high bandwidth use, connection counts, or server workload. When several of these symptoms occur unexpectedly at the same time, further investigation may be necessary to identify whether malicious traffic is involved.
Traffic patterns can provide additional clues, such as unusually concentrated requests for one resource or unexpected activity from certain networks or locations. However, attackers may deliberately vary their traffic to resemble legitimate visitors. Effective detection therefore relies on analyzing several signals together rather than using one simple threshold as proof of a DDoS attack.
Why DDoS Attacks Are Dangerous for Businesses
Website downtime can immediately affect organizations that depend on online transactions. Ecommerce stores may lose sales, software companies can experience service interruptions, and financial platforms may become temporarily inaccessible to customers. Even relatively short disruptions can create support requests, abandoned purchases, and frustration among users who expect services to remain consistently available.
DDoS incidents can also damage trust. Customers may not understand why a service is unavailable or whether their personal data is at risk, even when the attack only affects availability. Repeated outages can create concerns about reliability, particularly for organizations that provide essential online tools, subscriptions, financial services, or business-critical applications.
Operational costs may increase during and after an incident as technical teams investigate traffic, scale infrastructure, communicate with service providers, and restore normal operations. Businesses may also need additional security resources afterward. For this reason, DDoS protection is part of broader business continuity planning rather than merely a technical concern for cybersecurity teams.
How Security Teams Investigate DDoS Incidents
Security teams begin by determining whether unusual traffic represents an attack or legitimate demand. They review network monitoring, server performance, application logs, request patterns, and infrastructure alerts. Comparing current behavior with normal baselines can help distinguish an intentional overload from organic traffic generated by a campaign, product launch, or unexpected surge in public interest.
During analysis, teams may need to organize large amounts of technical information quickly. Research and summarization resources, including suitable AI research tools, can support broader investigation workflows when used carefully and without exposing sensitive data. However, security decisions should still rely on verified telemetry, established incident procedures, and experienced technical judgment.
Investigators also examine when the event started, which systems are affected, and whether traffic characteristics change over time. This information can help defensive services adjust filtering and identify the most affected infrastructure. Accurate records are also valuable after the incident because teams can review what worked, what failed, and which protections need improvement.
How DDoS Mitigation Works
DDoS mitigation attempts to separate malicious traffic from legitimate requests while keeping the targeted service available. Defensive systems may analyze traffic patterns, request behavior, reputation information, and other signals before allowing traffic to reach protected infrastructure. The challenge is blocking harmful activity without preventing genuine customers from accessing the website or application.
Large-scale mitigation services can absorb or process substantial traffic before forwarding legitimate requests toward the intended destination. Content delivery networks and distributed infrastructure can also spread demand across multiple systems instead of relying entirely on one origin server. This additional capacity can make it harder for a sudden traffic surge to overwhelm a single point.
Rate limiting and application-level controls may further reduce pressure by restricting excessive requests under defined conditions. Effective mitigation usually combines several techniques because no single control addresses every kind of DDoS traffic. Organizations should choose defenses based on their infrastructure, normal traffic volume, application design, and potential impact of downtime.
Use CDNs and Scalable Infrastructure
A content delivery network, or CDN, distributes web content across infrastructure located in multiple regions. Visitors can receive cached resources from systems closer to them rather than every request reaching the same origin server. This architecture can improve normal website performance while also providing additional capacity during large traffic surges.
Scalable cloud infrastructure can also help services adapt when demand increases. However, simply adding server capacity is not a complete DDoS strategy because sufficiently large or targeted attacks may still overwhelm resources or create unexpected costs. Scaling should be combined with filtering, monitoring, access controls, and dedicated protections designed to handle abusive traffic.
Organizations should understand where potential bottlenecks exist before an incident happens. A website may have powerful application servers while still depending on a smaller network connection or critical backend resource. Capacity planning helps security and infrastructure teams identify weaknesses that could otherwise become points of failure during sudden traffic increases.
Monitor Traffic Before an Attack Happens
Knowing what normal traffic looks like makes abnormal behavior easier to recognize. Organizations should monitor typical request volumes, bandwidth use, geographic patterns, application performance, and common traffic peaks. These baselines provide useful context when alerts suddenly show activity far outside ordinary levels and help teams decide whether an incident requires immediate investigation.
Automated alerts can notify teams when important thresholds are exceeded or unusual patterns appear. Alerts should be designed carefully so normal traffic spikes do not constantly trigger unnecessary emergencies. Excessive false alarms can cause alert fatigue, making it harder for administrators to recognize the events that genuinely require rapid action.
Monitoring should cover more than the public homepage. APIs, login services, checkout systems, DNS infrastructure, and other essential components can affect overall availability. Understanding dependencies helps teams detect attacks that target less visible parts of the service rather than simply generating obvious traffic against the main website.
Create a DDoS Response Plan
A DDoS response plan explains what the organization should do when signs of an attack appear. It should identify the people responsible for investigation, communication, mitigation, and escalation. Contact details for hosting companies, cloud providers, internet service providers, and security vendors should be readily available rather than gathered during an active incident.
The plan should also establish which services are most critical and how teams will prioritize them during disruption. Businesses may need to protect customer logins, transactions, communication systems, or core application features before less essential resources. Clear priorities help reduce confusion when infrastructure is overloaded and multiple teams need to make decisions quickly.
Practice the plan through exercises rather than assuming it will work perfectly during a real attack. Simulated scenarios can reveal missing contacts, unclear responsibilities, monitoring gaps, or communication problems. Lessons from these exercises can then be used to strengthen procedures before customers and business operations depend on them during an actual incident.
DDoS Attacks vs DoS Attacks
A denial-of-service, or DoS, attack and a distributed denial-of-service attack share the same basic objective: making a service unavailable. The main difference is where the malicious traffic originates. A traditional DoS attack generally relies on a more limited source, while a DDoS attack distributes activity across many systems.
The distributed nature of DDoS attacks can make mitigation more difficult because simply blocking one source may have little effect. Traffic may originate from thousands of devices across different networks. Defenders need mechanisms that recognize harmful behavior while continuing to accept legitimate requests from users who may share similar locations or internet providers.
Both attacks target availability rather than necessarily stealing information. However, security teams should not assume that availability disruption is the only activity occurring during an incident. Organizations still need broader monitoring because attackers may combine distraction, credential attacks, or other malicious behavior with a service disruption.
Build a Layered Defense Against DDoS Threats
No single security product guarantees complete protection from every DDoS attack. Strong defense combines monitoring, scalable infrastructure, traffic filtering, resilient architecture, rate controls, and an established response plan. The exact combination depends on the organization’s services, risk level, technical architecture, traffic patterns, and available security resources.
Businesses should also reduce unnecessary internet exposure and maintain secure configurations across their environments. Systems that do not need to be publicly accessible should not be exposed without reason. Regular security reviews can identify outdated services, weak configurations, or infrastructure dependencies that may make availability problems more difficult to manage during an attack.
Finally, defenses should evolve as the organization’s infrastructure changes. New applications, cloud migrations, APIs, geographic expansion, and increases in legitimate traffic may alter previous assumptions about capacity and risk. Reviewing DDoS protections regularly helps ensure that safeguards designed for yesterday’s infrastructure still match the systems the business relies on today.
Conclusion
A DDoS attack is an attempt to overwhelm a website, application, network, or online service with enough distributed traffic to make it slow or unavailable. Many attacks rely on large numbers of compromised devices working together. The target may struggle to serve legitimate users because bandwidth, computing power, connections, or application resources become exhausted.
Protecting against DDoS threats requires preparation rather than waiting until a major outage begins. Traffic monitoring, resilient architecture, content delivery networks, scalable resources, mitigation services, and careful access controls can reduce risk. A documented incident response plan also helps teams react faster when abnormal traffic threatens important services.
DDoS attacks cannot always be prevented entirely, but their business impact can often be reduced through layered defenses and careful planning. Organizations should understand their normal traffic, identify critical systems, monitor unusual behavior, and regularly review protection strategies. Strong availability security helps keep digital services reliable even when they face unexpected or intentionally disruptive traffic.
FAQs
What is a DDoS attack in simple terms?
A DDoS attack overwhelms an online service with traffic from many different devices. The excessive activity consumes available resources and can make the website or application slow or unavailable to legitimate users.
What is the main purpose of a DDoS attack?
The primary purpose is usually to disrupt availability rather than directly steal information. Attackers attempt to prevent legitimate users from reaching a website, application, network, or other online service.
How can you tell if a website is under a DDoS attack?
Possible signs include sudden traffic spikes, slow performance, repeated timeouts, high bandwidth consumption, and unexpected service outages. Technical monitoring is required because legitimate traffic surges can sometimes create similar symptoms.
Can a CDN help stop DDoS attacks?
A CDN can distribute traffic across multiple systems and provide additional filtering and capacity. It can be an important defense layer, although effective DDoS protection usually requires several mitigation techniques working together.
Are DDoS attacks the same as hacking?
DDoS attacks are a form of cyberattack, but they usually focus on disrupting service availability rather than gaining unauthorized access. An attacker may still combine a DDoS incident with other malicious activity.